Device intelligence for fraud and risk teams
See the device behind a session.
Add Noxtica to your site. It collects browser, device, network and behavior signals and returns a risk score. Where enabled, you also get named reasons and a confidence level. Your policy decides what happens next.
Scores and reasons are probabilistic estimates, not statements of fact. Your team makes every decision.
How it works
Three steps from your site to your own decision.
Add Noxtica to your site.
A script or SDK collects browser, device, network and behavior signals.
Get a risk score.
Each assessment has a risk score. Named reasons and a confidence level appear where enabled for your account.
Your policy decides.
Your policy can allow, block, ask for extra verification or send the session to review. Noxtica never decides for you. Every action comes from the policy you set.
Example · synthetic workspace
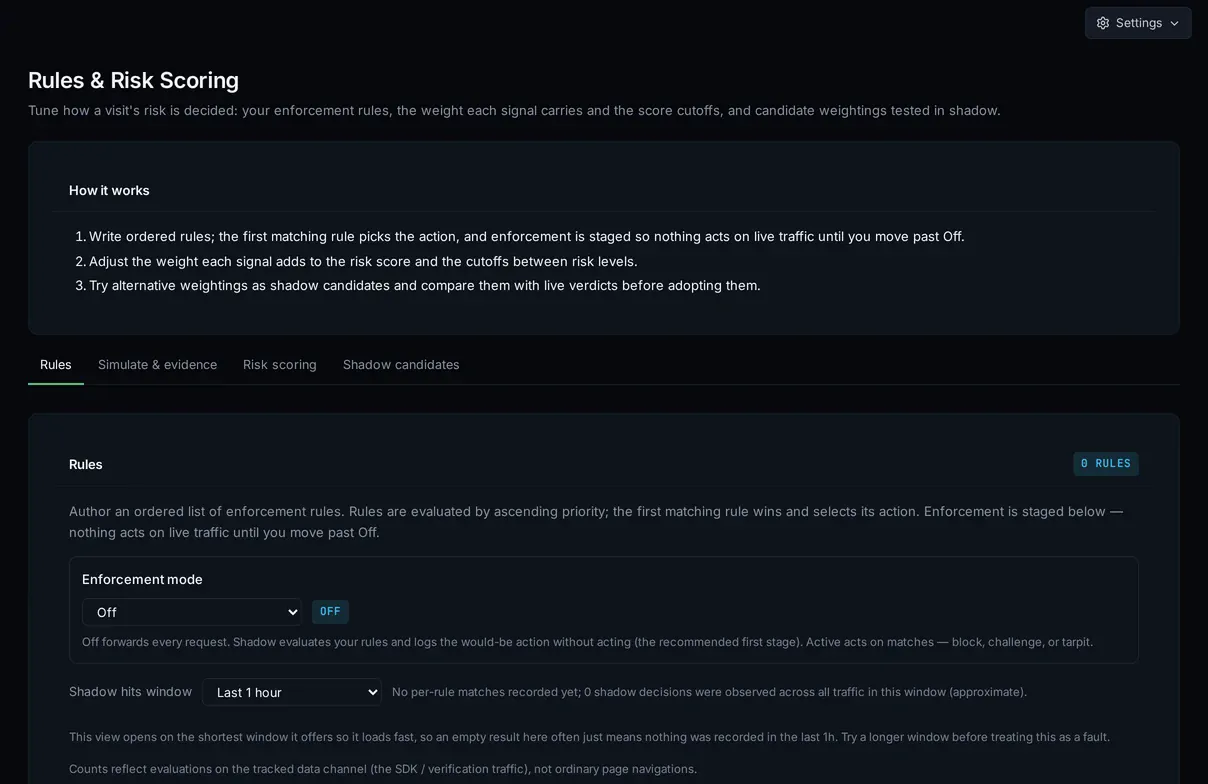
What happens in this recording
- Rules & Risk Scoring: ordered rules, signal weights and risk-level cutoffs, with enforcement staged from Off to Shadow to Active.
- Risk Actions: observe-only evidence of would-be actions, with counters, shown before a policy is switched from Shadow to Active.
- Script & Consent: collector script snippets, consent settings and protected actions for a domain.
Three Backoffice screenshots from a test workspace with synthetic data, shown in a loop; not a recording of a person using the product. Figures on the screens are test data, not results from any customer. The interface on the screens is in English.
What you get
Three groups of products. Each product is Available or in Early Access.
Know the device and identity
See the device behind a session, and check the person or AI agent when you need to.
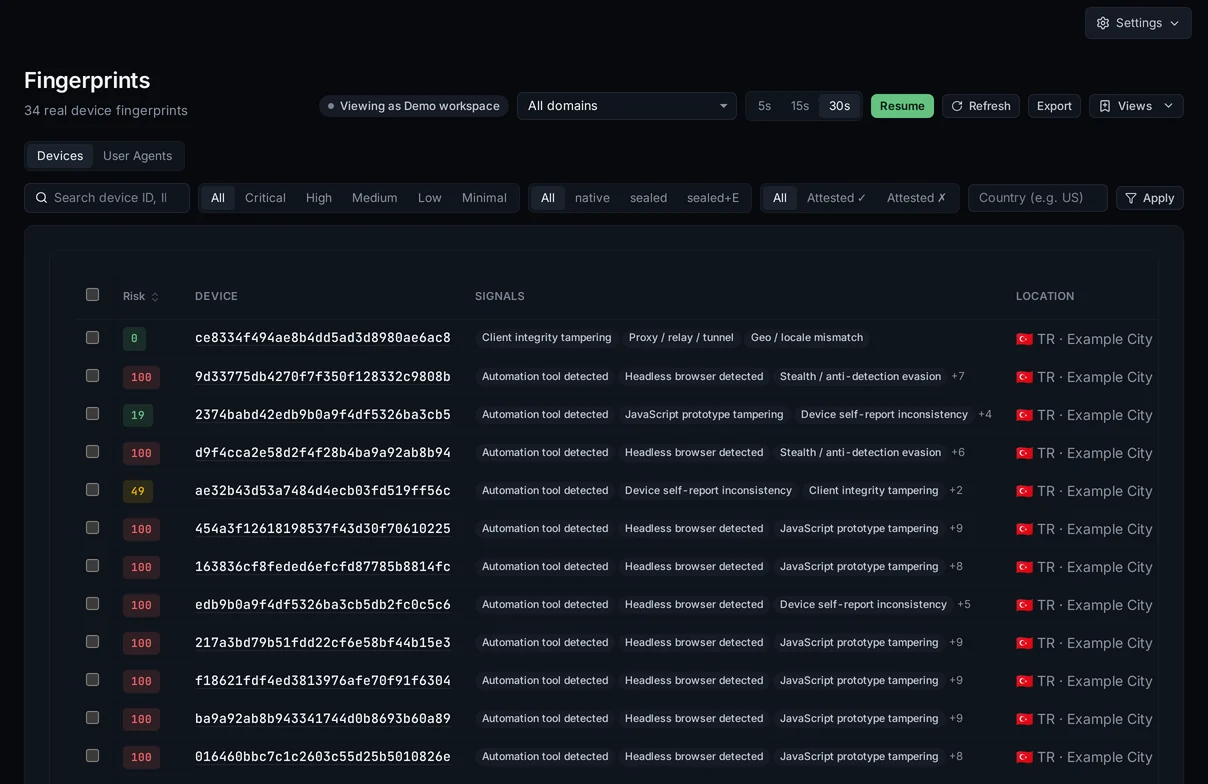
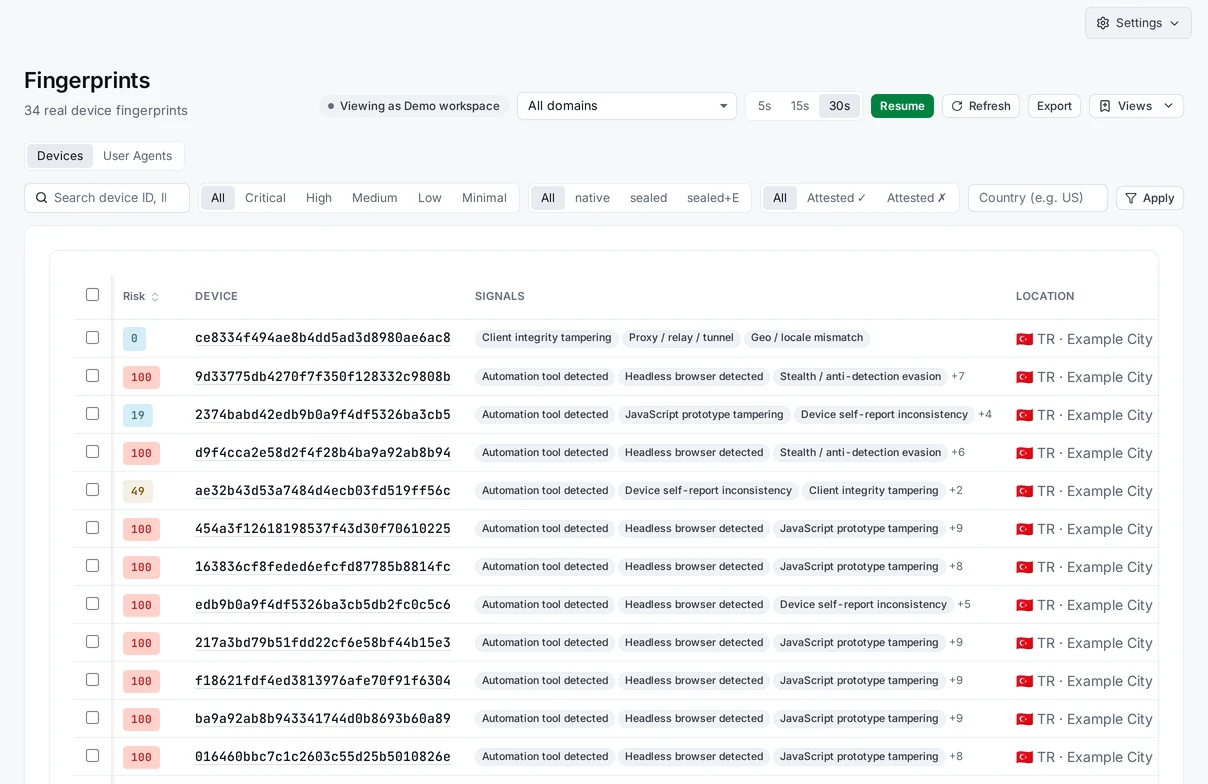
Device list in BackofficeSynthetic data from a test workspace - Device IntelligenceAvailableRecognize returning devices and review the signals for each device.
- Identity VerificationAvailableHosted identity verification, with the decision left to you.
- Know Your AgentEarly AccessVerify signed agents before you decide how to treat them.
- ID WalletEarly AccessReuse a verified identity, with consent for each share.
Understand the risk
Get a risk score. Named reasons and a confidence level are added where enabled.
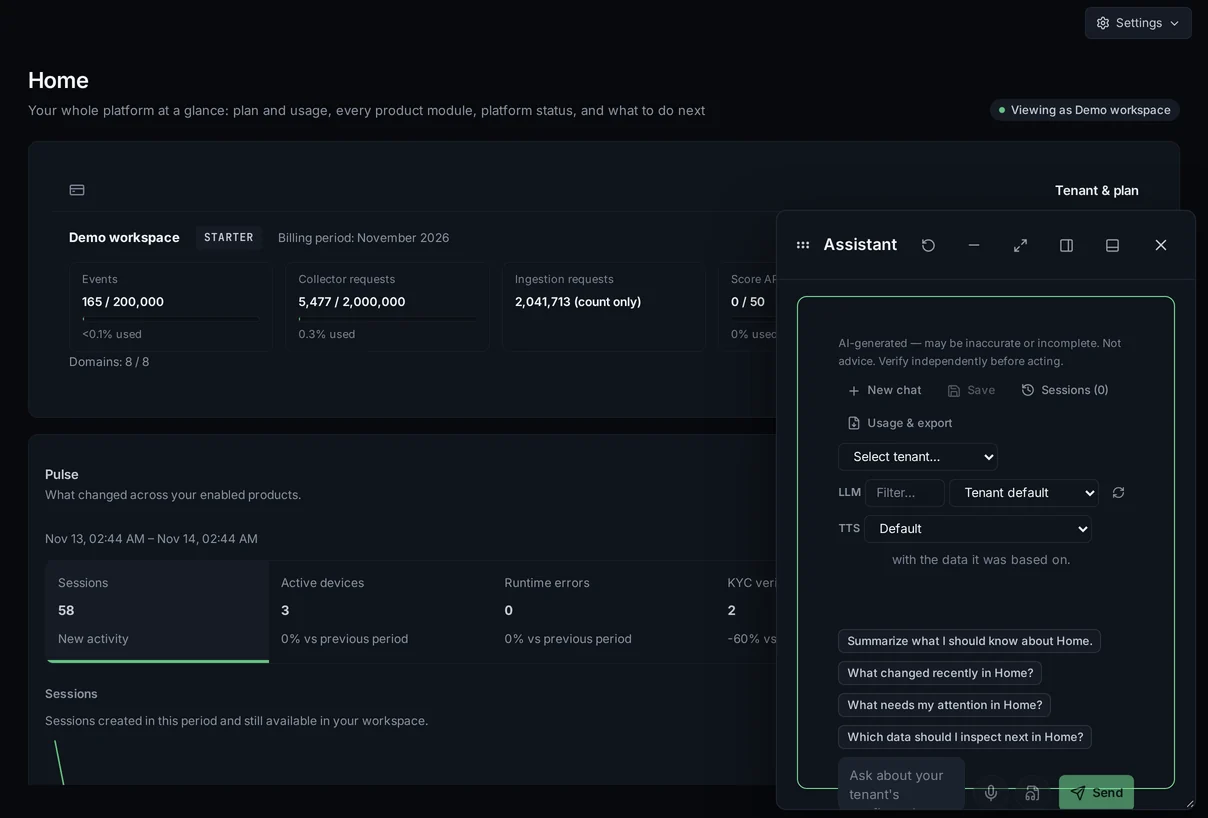
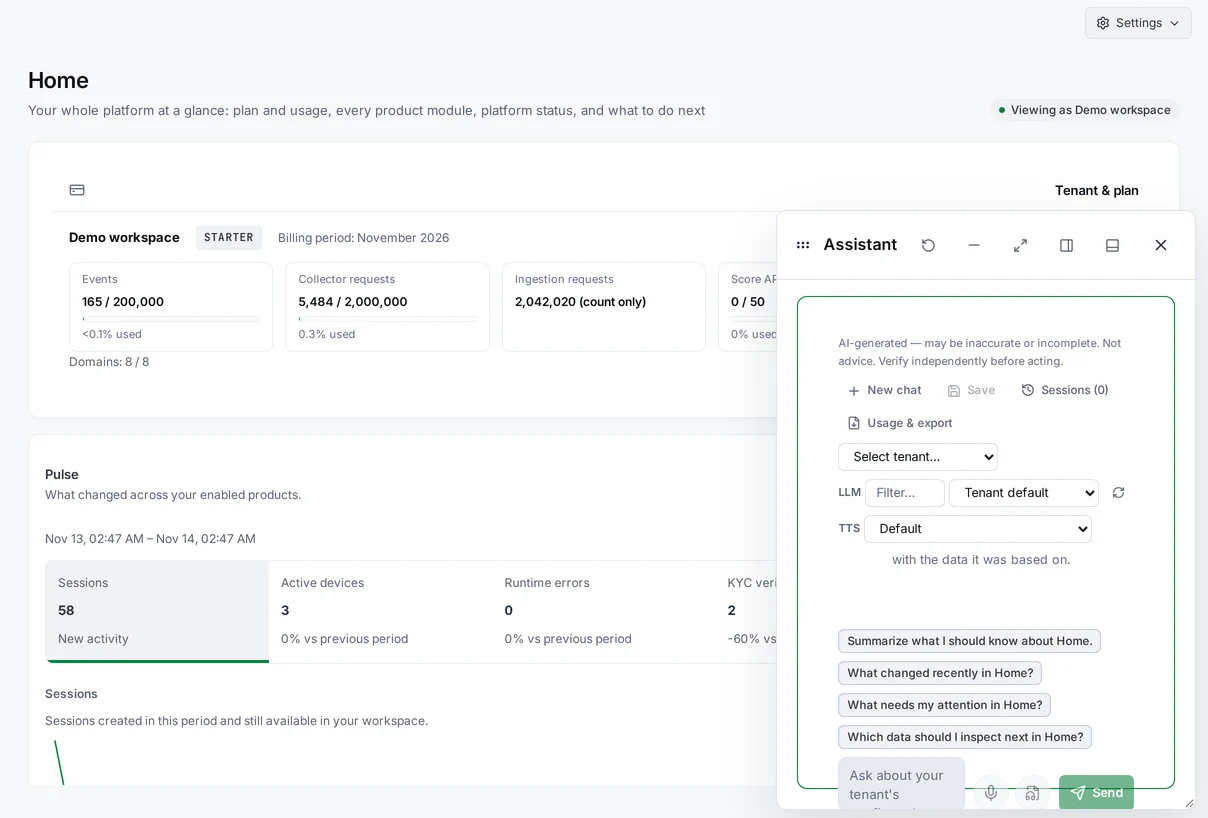
AI Assistant in the back officeSynthetic data from a test workspace - Risk ScoringAvailableA risk score with a level, plus confidence and named reasons where enabled.
- AI AssistantAvailableRead-only assistant for operators. People make every decision.
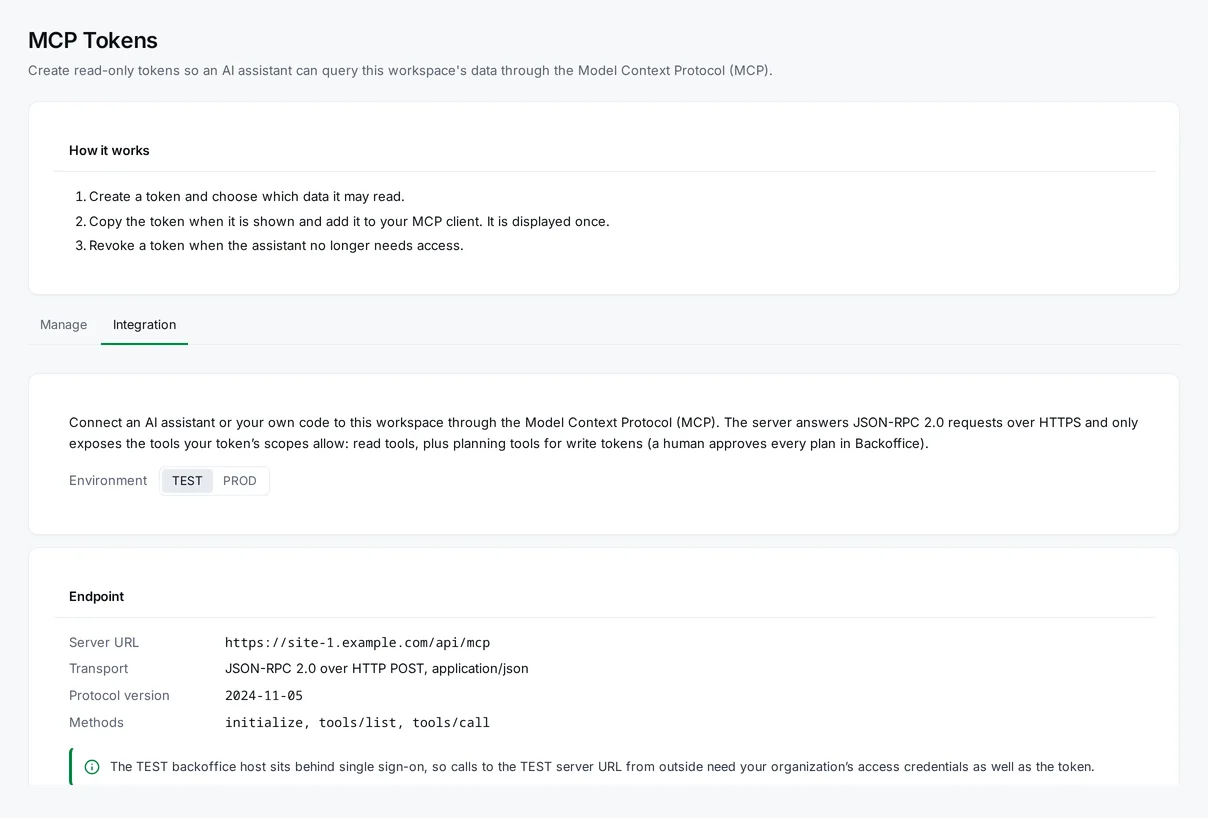
- MCP ServerAvailableRead-only MCP over the tenant's own risk telemetry.
See what happened
Replay recorded sessions and monitor real user experience.
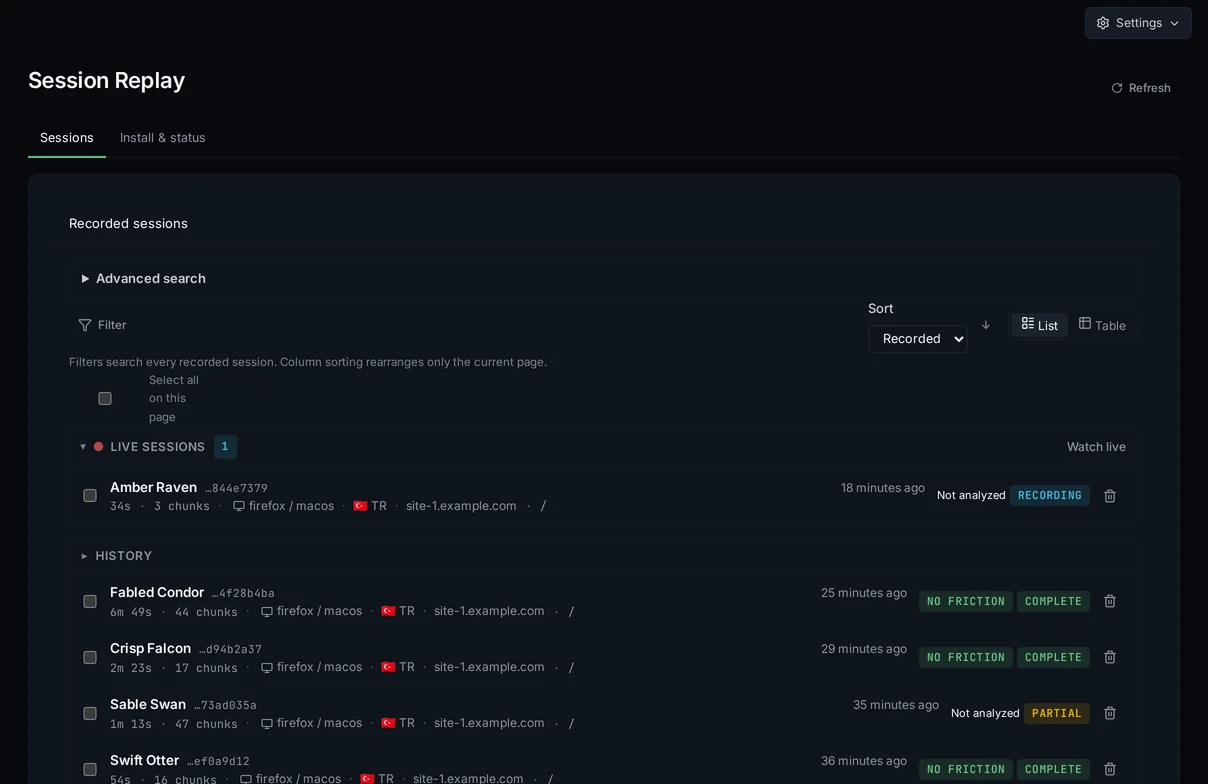
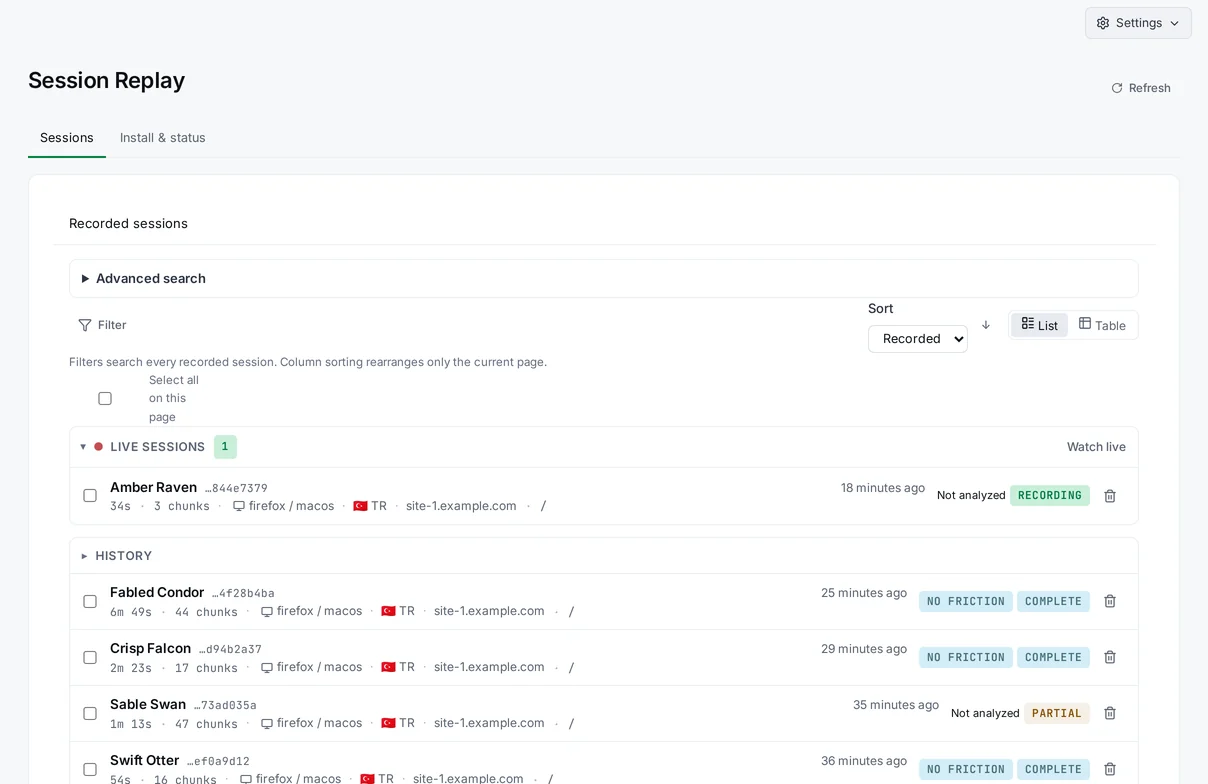
Session list in BackofficeSynthetic data from a test workspace - Session ReplayAvailableReplay recorded sessions in Backoffice, beside risk and diagnostic context.
- Real User MonitoringAvailableSee how your pages perform for real visitors.
- APMEarly AccessLink slow pages to the server work behind them.
- PulseEarly AccessEndpoint signals that device owners can see.
- SEO/AEO & MarketingEarly AccessTechnical SEO and answer-engine readiness checks.
Your policy decides. Noxtica never decides for you.
Common scenariosAccount takeoverSignup abuseAutomated agents
Product examples
Real screens, synthetic data
Short recordings of the product’s own screens, made in a test environment with synthetic data.
Risk Analytics in the Backoffice
Example · synthetic workspace
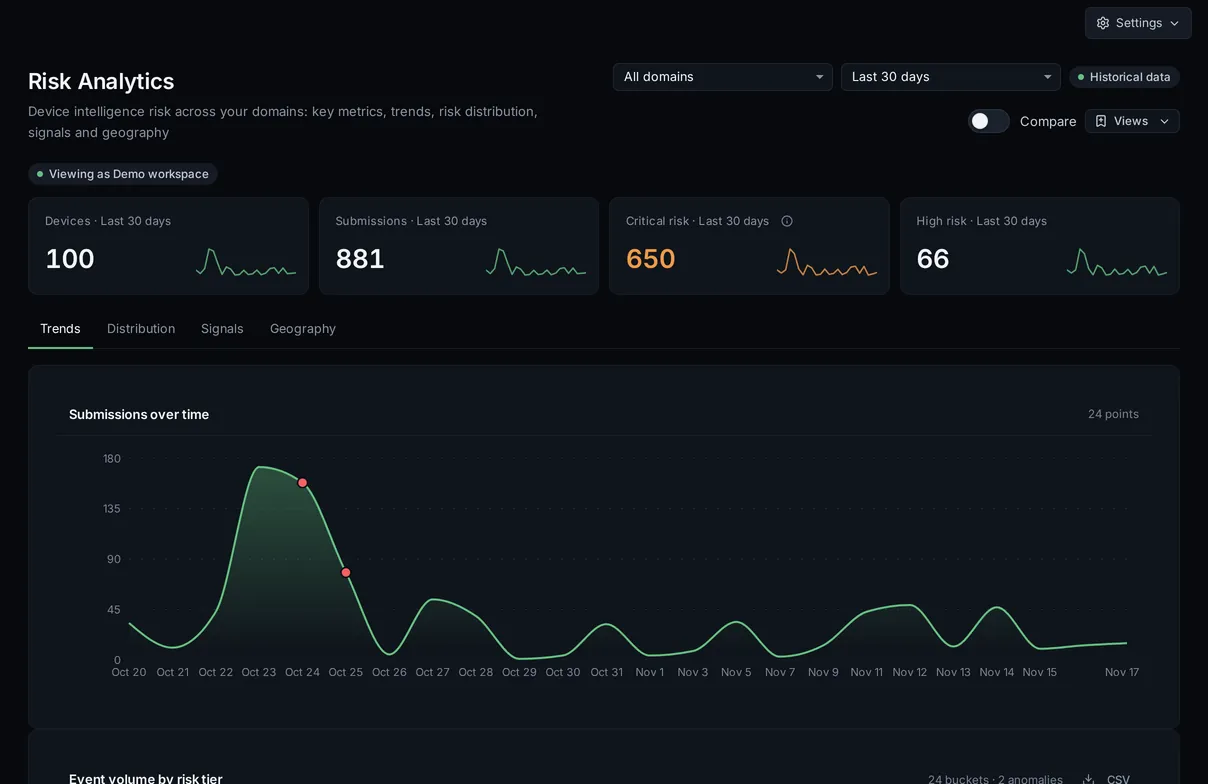
What happens in this recording
- Risk Analytics opens on the last 30 days, with totals for devices, submissions, critical risk and high risk.
- The Trends tab shows a line chart of submissions over time.
- The Distribution tab counts submissions for each risk level, from Critical to Minimal, next to a breakdown by country.
Recorded from the Backoffice in a test workspace with synthetic data. Most of the traffic was generated by automated test browsers, so the high share of Critical ratings reflects the test setup, not typical traffic. The figures and the country breakdown describe that test traffic, not any customer or live site. Identifiers were replaced with synthetic values. These screens illustrate the interface, not detection accuracy. The interface in the recording is in English.
A device record in the Backoffice
Example · synthetic workspace
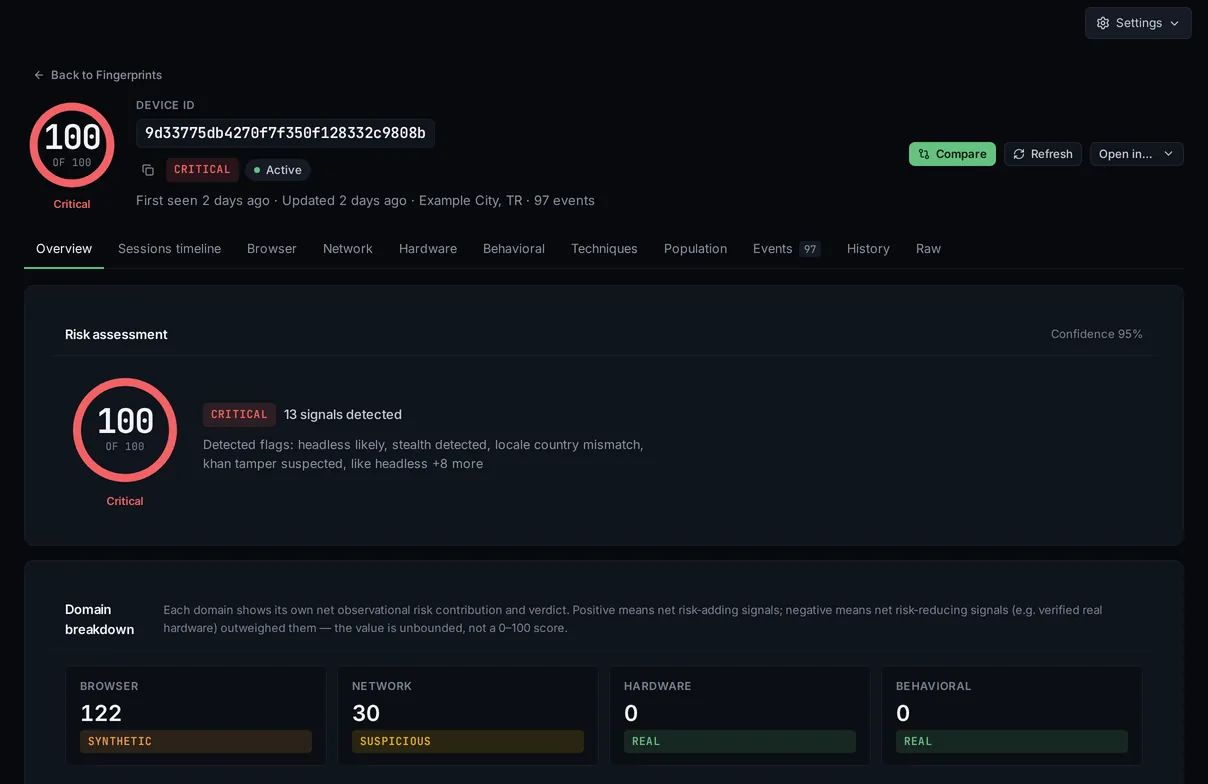
What happens in this recording
- The record opens on the Overview tab: the device ID, a risk score out of 100, the risk level, the number of signals and the risk flags raised.
- The domain breakdown shows browser, network, hardware and behavioral values, each with one of the product’s own labels: “Real”, “Suspicious” or “Synthetic”. These labels are unrelated to the “synthetic workspace” label. The values are not scores from 0 to 100.
- The Behavioral tab lists measurements collected during the session.
- The History tab lists the submissions recorded under this device ID in the test workspace: time, risk level, score and risk flags.
Recorded from the Backoffice in a test workspace with synthetic data. The device shown is an automated test browser, so its score reflects that setup. Its history shows repeated test runs and does not demonstrate recognition across sessions. The recording illustrates the interface, not detection accuracy or any customer’s data. Identifiers, locations and addresses were replaced with synthetic values. The interface in the recording is in English.
The hosted verification flow, step by step
Synthetic person · specimen document · simulated liveness
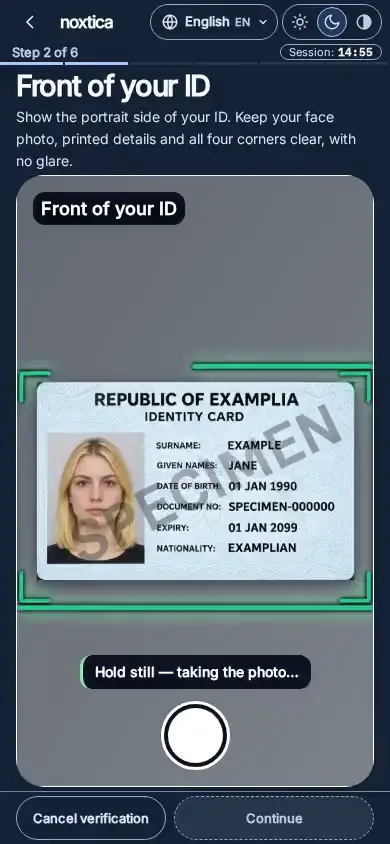
What happens in this recording
- The consent screen is shown and accepted.
- The front of a fictional specimen ID card is captured.
- The back of the card is captured.
- A selfie is captured.
- The liveness prompts appear: look up, tilt the head down, turn left, turn right. The same AI-generated face is shown in each pose, as in a mirrored camera preview. This step is simulated in the recording.
- The final screen reads “Your verification is under review.” In live use, the organization that requested the check reviews the submission. This screen is not an approval.
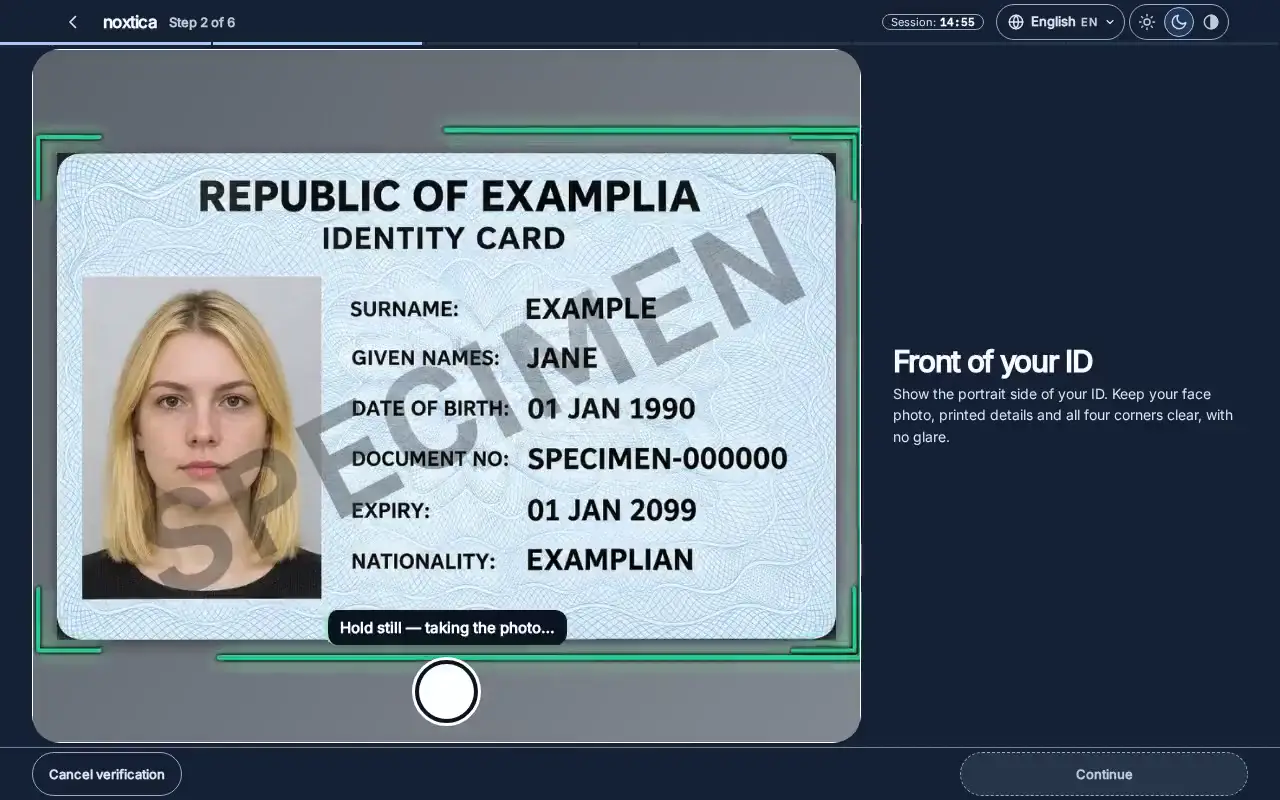
What happens in this recording
- The consent screen is shown and accepted.
- The front of a fictional specimen ID card is captured.
- The back of the card is captured.
- A selfie is captured.
- The liveness prompts appear: look up, tilt the head down, turn left, turn right. The same AI-generated face is shown in each pose, as in a mirrored camera preview. This step is simulated in the recording.
- The final screen reads “Your verification is under review.” In live use, the organization that requested the check reviews the submission. This screen is not an approval.
A recording of the real hosted flow in a test environment. The face and its head poses are AI-generated images and the ID is a fictional specimen. The liveness step is simulated: no biometric analysis ran and nothing was sent to a reviewer. This is not a real verification result. The interface in the recording is in English, and playback is sped up.
How pricing works
Start with one base package. Add products and capacity when you need them.
Base package
Every account has one base package. It includes monthly usage allowances.
Products
Device Intelligence, AI Assistant and MCP Server are included in every base package. Other products, including Risk Scoring, are billed at their listed unit price, or in a monthly package arranged with our team.
Capacity and usage
Extra capacity is optional. Usage beyond your allowances is billed at the listed unit price where one applies.
Evidence
What you can verify today
Product availability
Products with stated availability: 12
Each product page states how it is offered.
Explore products and availabilityRisk outputs
Risk levels: 5
Detection Signals documents the levels. Where enabled, an assessment also carries confidence and named reasons.
Read Detection SignalsPrivacy
No sale of personal data, and no advertising
The Privacy Policy states we sell no personal data and serve no advertising.
Read the Privacy PolicyDecision ownership
Advisory: risk scores, not decisions
The Risk Intelligence page states that customer-owned policy sets the action.
Read the Risk Intelligence page
Integration
Collect in the browser, decide in your application
Your server performs the authenticated read. Your application owns the policy and every final decision.
Collector snippet
Load the collector with an origin-bound public Site Key.
<script
  src="https://collect.noxtica.com/collector/noxtica-collector-core.js"
  data-site-key="pk_prod_your_site_key_here"
  data-auto-init
  data-auto-check-once
  async
></script>
Server lookup
Read the device record with a server-held key.
curl "https://collect.noxtica.com/v1/device/example-deviceId" \
  -H "Authorization: Bearer $NOXTICA_API_KEY"
MCP config
Read-only, opt-in MCP with an operator-issued, scoped token.
# Synthetic secret; requires separately provisioned MCP access.
curl -X POST 'https://backoffice.noxtica.com/api/mcp' \
  -H 'Authorization: Bearer mcp_SYNTHETIC_NOT_A_REAL_TOKEN' \
  -H 'Content-Type: application/json' \
  -d '{"jsonrpc":"2.0","id":1,"method":"tools/list"}'
An MCP session, start to finish
An MCP client adds the server, lists the tools its token may call and makes one read-only call. The token, the device handle and the result are examples.
export NOXTICA_MCP_TOKEN=mcp_example_not_a_real_tokenclaude mcp add --transport http noxtica https://backoffice.noxtica.com/api/mcp \ --header "Authorization: Bearer $NOXTICA_MCP_TOKEN"curl -s -X POST https://backoffice.noxtica.com/api/mcp \ -H "Authorization: Bearer $NOXTICA_MCP_TOKEN" \ -H "Content-Type: application/json" \ -d '{"jsonrpc":"2.0","id":1,"method":"tools/list"}' \ | jq -r '.result.tools[].name' \ | grep -E '^(get_risk_distribution|get_score_explanation|list_alerts)$'get_risk_distributionget_score_explanationlist_alertscurl -s -X POST https://backoffice.noxtica.com/api/mcp \ -H "Authorization: Bearer $NOXTICA_MCP_TOKEN" \ -H "Content-Type: application/json" \ -d '{"jsonrpc":"2.0","id":2,"method":"tools/call","params":{"name":"get_score_explanation","arguments":{"limit":1}}}' \ | jq -r '.result.content[0].text | fromjson | .data.entries[0]'{ "deviceId": "dev_demo_0001", "score": 8, "band": "minimal", "confidence": 0.9, "reasons": []}Example read-only session: the tool list, filtered here to three read tools, and one call that returned the score of device dev_demo_0001: band minimal (the risk level), score 8, confidence 0.9, no reason codes.
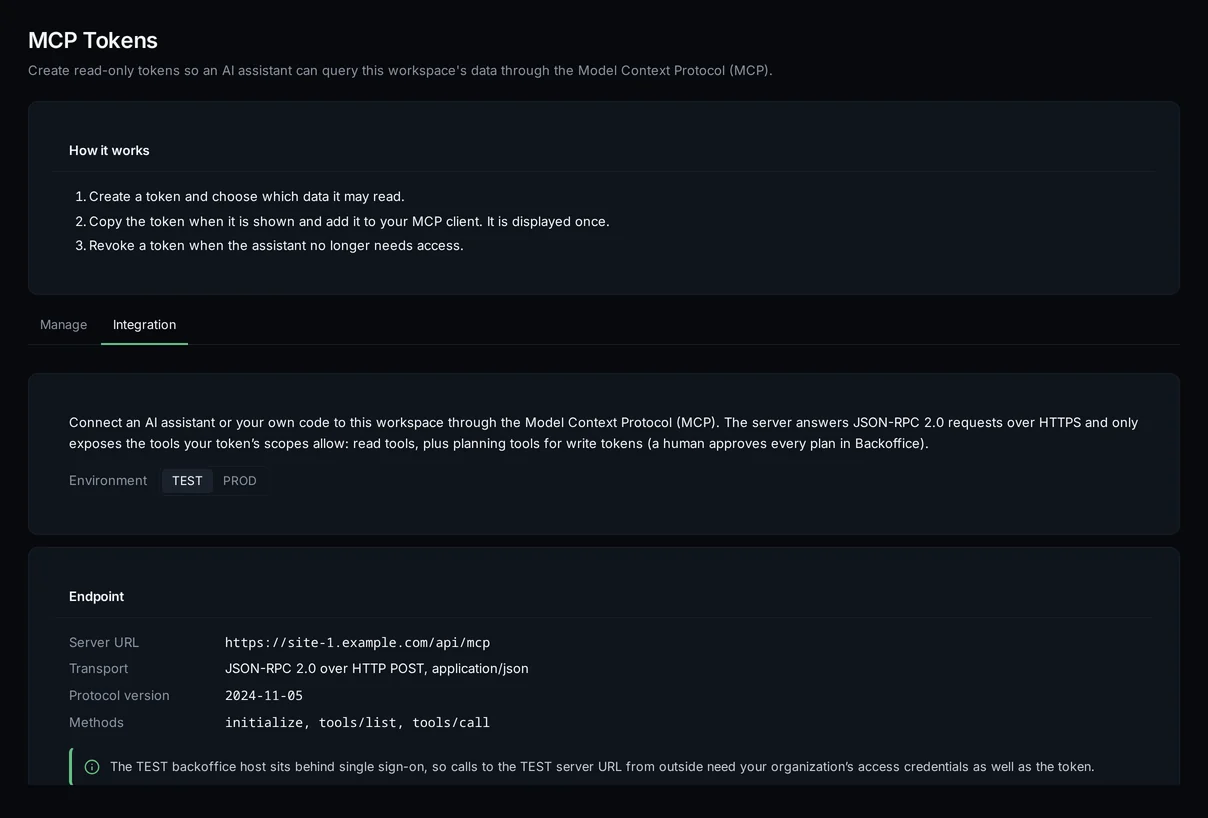
The public browser collector needs no package.
Data practices
Our security, privacy and subprocessor documents are public
You set consent and masking
Replay starts after policy, legal-basis, DNT, GPC, sampling and consent gates admit it.
Review privacy controlsRetention varies by data class
Backoffice shows the retention and data locations in force for your workspace. Your contract and the DPA hold the commitments.
Review retention and locationsThe operator and its providers are named
NoxRed LLC operates Noxtica. The DPA and the subprocessor list are public.
View subprocessors
Scores and reasons are probabilistic estimates, not statements of fact. Your team makes every decision.
The thinking behind the score.
Read the whitepapersQuestions and answers
Is a Noxtica risk score a verdict?
No. Noxtica returns a risk level, confidence, and reasons. Your team owns the policy and makes the final call.
How are Noxtica products made available?
Available products are either enabled for every workspace or enabled for your account on request; each product page says which. Early Access products are not generally available and carry no service level and no commitment on scope or timing.
Does identity verification approve people automatically?
No. Automated hosted verification ends in manual review. PAD and liveness checks provide advisory signals, not approval.
Where do you store data, and how long do you keep it?
Both depend on the data class and configuration. Backoffice shows retention and data locations for your workspace. The privacy policy and subprocessor list name providers and regions.
Walk through one real decision
Bring the interaction your team cannot afford to misread.
We will review the product view, relevant evidence and limits, integration responsibilities, and practical evaluation next steps.
Request a walkthrough